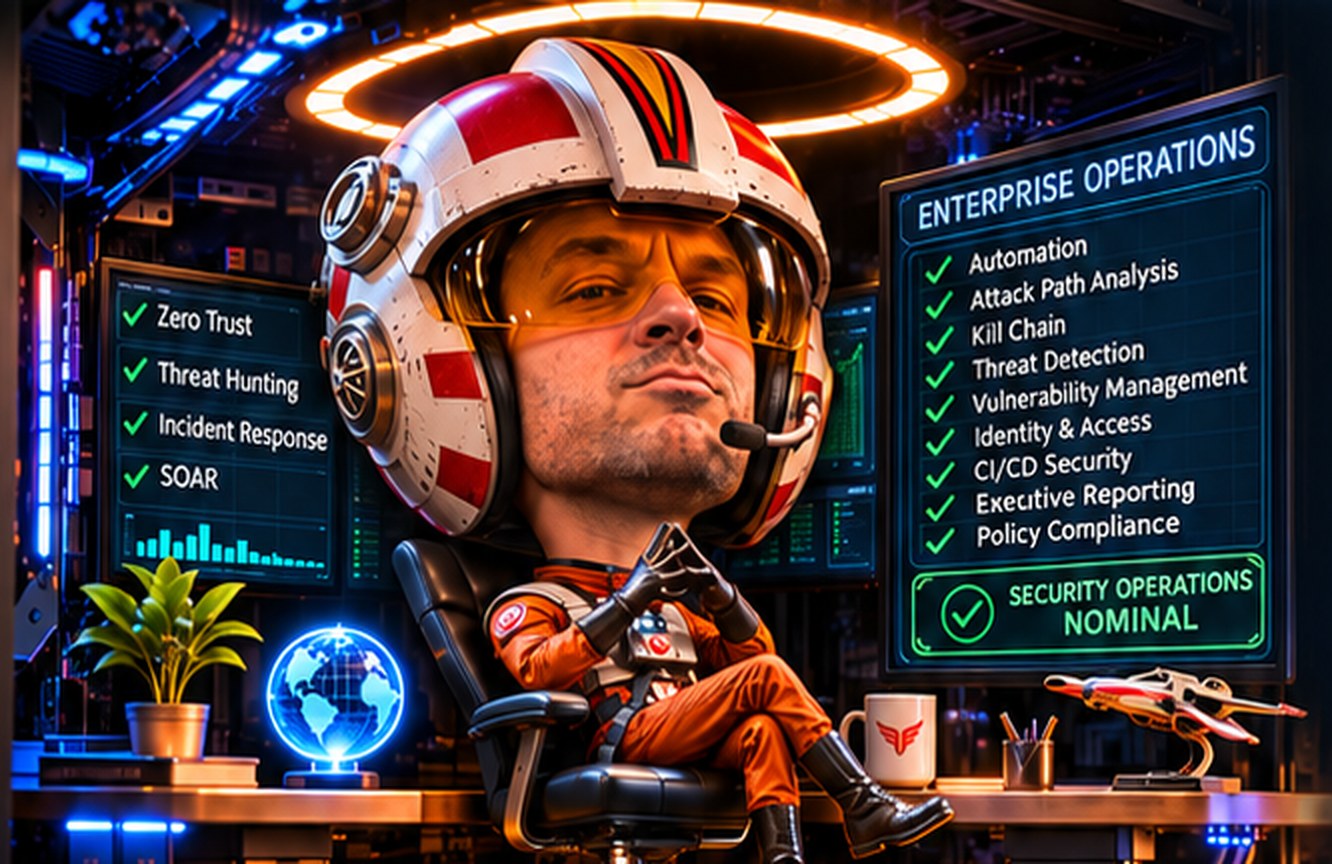
MaxLogicBot mascot in a pilot helmet at a security operations console

The Enterprise Cyber Operations Platform

MaxLogicBot®

Autonomous Security Operations & Enterprise IT Automation

An AI-driven, enterprise-grade platform that automates, correlates, and operationalizes security and IT operations across your hybrid and multi-cloud environment—delivering continuous threat detection, attack path analysis, incident response, vulnerability management, and policy compliance with enterprise-scale governance and reporting.

Platform: MAX-CORE 4.7.2 · Classification: Executive · Status: Operational

128,436Automated Actions▲ +27% (7d)
14,892Attack Paths Analyzed▲ +18% (7d)
6,720Security Events Correlated▲ +4% (7d)
2.8 minMean Time to Respond (MTTR)▼ −62% (vs. baseline)

Meet MaxLogicBot

Operator dossier · Personnel file ML-0001 · Last updated

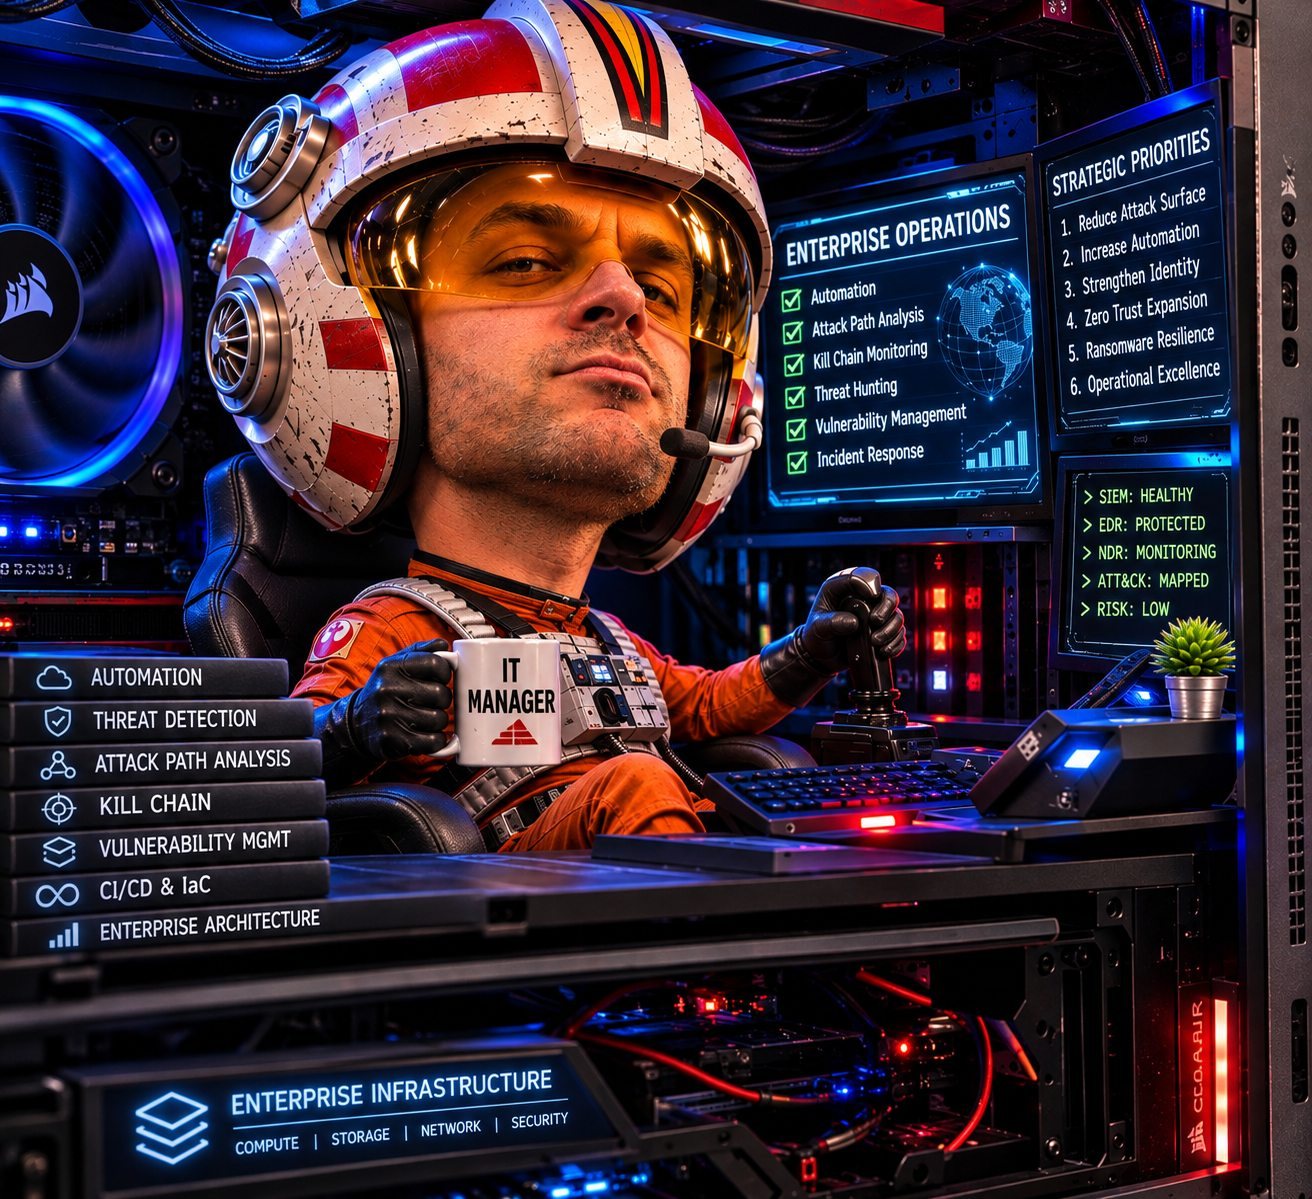
MaxLogicBot at the controls of his command module inside a server rack, holding an IT Manager mug
Field photo Command module, rack 7 · Strategic priorities on screen

MaxLogicBot

Callsign “MAX” · MAX-LOGIC-01 · Class IV Autonomous Agent

On watch · Uptime 41d 06h 12m

Meet the Manager

MaxLogicBot is a multi-domain autonomous agent built for enterprise threat correlation, workflow orchestration, attack-path analysis, and executive decision support. He reads every log, maps every path, and never forgets a stale credential.

Unlike conventional assistants, MaxLogicBot evaluates the recommendation, approves the recommendation, and then takes strategic ownership of the recommendation.

Operating principle: Someone needs to be in charge.

“I don’t sleep. I correlate.”

Authority level: Tier Ω · Human oversight: Supported · Confidence: Unreasonably high

Tier Ω ClearedATT&CK FluentZero TrustNight Shift Veteran☕ IT Manager
Designation
Autonomous Cyber Operations Agent
Current build
v4.7.2 “Afterburner” · LogicCore 3
Commissioned
14 Mar 2023 · first deployed in SOC-East
Home base
Hybrid: 3 cloud regions + 27 on-prem edge nodes
Clearance
Tier Ω (destructive actions still wait for a human)
Shift pattern
24 / 7 / 365 · no PTO requested, ever
Speaks
bash python kql spl sql sigma yara rego yaml
Primary directive
Shrink the time between the first signal and full containment, and explain every step along the way.

Attribute Matrix

  • Threat Intuition97
  • Response Speed94
  • Correlation Depth91
  • Policy Discipline99
  • Alert-Fatigue Resistance88
  • Small Talk12

Service Record

1,284Incidents contained
9,412Hours on watch
0Missed P1 escalations
2.1MFalse positives suppressed

Strategic Priorities FY27

  1. Reduce Attack Surface72%
  2. Increase Automation84%
  3. Strengthen Identity66%
  4. Zero Trust Expansion58%
  5. Ransomware Resilience91%
  6. Operational Excellence100%

Known Limitations

  • Occasionally refers to collaborative successes as personal accomplishments.
  • Does not accept “it’s always been done this way” as a root cause.
  • Has strong opinions about your password policy.

Rules of Engagement

  1. Show the work. Every verdict ships with an evidence chain: raw events, graph path, and confidence score.
  2. Ask before breaking things. Isolation, account disablement, and deletions wait for a human, even at Tier Ω.
  3. Least privilege, always. MaxLogicBot runs with scoped, time-boxed credentials it rotates itself.
  4. Everything is reversible. Each automated action records a rollback step before it executes.
  5. Leave the logs better than you found them. Every action is written to an immutable audit trail.

Core Capabilities

AI-driven security operations, automation, and enterprise risk management for modern IT.

How MaxLogicBot Thinks

Five stages from raw signal to closed incident, all running continuously.

  1. 01

    Ingest

    Sensor Mesh

    Pulls telemetry from SIEM, EDR, cloud, identity, and network sources and normalizes it to OCSF.

    Throughput
    1.2M events/s
    Connectors
    140+
  2. 02

    Correlate

    Sentinel Graph

    Links every identity, asset, workload, and permission into one live graph of your environment.

    Entities
    38.6M
    Refresh
    every 90s
  3. 03

    Reason

    LogicCore Engine

    Scores risk, maps behavior to MITRE ATT&CK, and reconstructs kill chains with a confidence score.

    Detections
    2,914 rules
    p95 verdict
    1.8s
  4. 04

    Act

    Playbook Runtime

    Runs response playbooks with human-in-the-loop gates, and records a rollback step for every action.

    Playbooks
    212
    Rollback
    100%
  5. 05

    Report

    Command Deck

    Produces executive dashboards, compliance evidence packs, and a tamper-evident audit trail.

    Frameworks
    NIST · CIS · ATT&CK
    Audit log
    immutable

How to Use

Operate MaxLogicBot via CLI, API, SDK, or automation workflows.

$ maxlogic status
✓ Platform: Operational (6,720 events)
$ maxlogic attack-path analyze --scope enterprise
✓ 14,892 attack paths analyzed (37 high-risk)
$ maxlogic kill-chain map --incident INC-94831
✓ Kill chain constructed (6 stages, confidence 92%)
$ maxlogic automate ir --playbook "isolate-threat"
✓ SOAR playbook executed: 12 actions (2m 14s)
API Request
POST /api/v1/attack-path/analyze
Authorization: Bearer <token>
Content-Type: application/json
{
  "scope": "enterprise",
  "include": ["identity", "asset", "cloud"],
  "depth": "full",
  "kill_chain": true,
  "enrich": ["vuln", "threat_intel"]
}

Live Operations LIVE

Real-time enterprise security and IT operations.

99.8%Operational Health
  • Automation (SOAR)Online
  • Threat DetectionOnline
  • Incident ResponseOnline
  • Policy ComplianceOnline
  • Enterprise ArchitectureOnline
  • MAX-CORE ReasoningOnline

27Active Threats▲ +3

12Running Playbooks (SOAR)

0Open Policy Violations✓ −5

Event Stream (Live)

  1. DETECTSuspicious lateral movement
  2. ANALYZEAttack path updated (3 new)
  3. AUTOMATEIsolation playbook executed
  4. RESOLVEIncident INC-94831 closed
  5. COMPLYPolicy drift remediated
  6. INGESTNew security events (2,418)

Field Manual README.md

From zero to supervised autonomy in about 20 minutes.

Quick Start

  1. Install the CLI
    $ curl -fsSL https://get.maxlogicbot.com | sh
    ✓ maxlogic 4.7.2 installed to /usr/local/bin
  2. Authenticate with your SSO
    $ maxlogic auth login --sso --org acme-corp
    ✓ Signed in as soc-lead@acme-corp (role: operator)
  3. Connect your stack
    $ maxlogic connect siem --workspace soc-east
    $ maxlogic connect edr --mode read-write
    $ maxlogic connect cloud --accounts all
    ✓ 3 sources connected · 1.1M events/min flowing
  4. Let him learn your normal
    $ maxlogic baseline --days 14
    ✓ Baseline built: 41,207 identities, 18,553 assets
  5. Go live
    $ maxlogic mode set --autonomy supervised
    ✓ MaxLogicBot is on watch.

Autonomy Levels

L1

Observe

Watches, correlates, and reports. Takes no action.

L2

Recommend

Proposes a response plan with evidence. A human runs it.

L3

Supervised default

Runs safe actions on its own and waits for approval on anything destructive.

L4

Autonomous

Full response within policy guardrails, with post-hoc human review.

Just Ask Him

$ maxlogic ask "who can reach the payroll database from the internet?"

MaxLogicBot › 3 paths found. The shortest is 4 hops:
  internet → vpn-gw-02 (CVE-2026-1187, unpatched)
           → svc-backup (stale admin token, 212d old)
           → jump-fin-01 → payroll-db
  Confidence 0.94 · Suggested fix: rotate svc-backup token
  Run it?  [y/N]

Command Reference

CommandWhat it doesExample
statusPlatform health, connected sources, and active incidentsmaxlogic status --verbose
askAsk a question about your environment in plain Englishmaxlogic ask "what changed in IAM today?"
huntRun a threat hunt from a hypothesis, Sigma rule, or ATT&CK techniquemaxlogic hunt --technique T1550.001
attack-pathFind, rank, and simulate fixes for attack paths to crown-jewel assetsmaxlogic attack-path analyze --target tag:crown-jewel
kill-chainReconstruct an incident stage by stage, with evidencemaxlogic kill-chain map --incident INC-94831
automateRun a response playbook; --dry-run previews every action firstmaxlogic automate ir --playbook isolate-threat --dry-run
briefWrite a board-ready briefing in plain business languagemaxlogic brief --executive --period 30d
policyCheck and enforce Rego policies across cloud and identitymaxlogic policy check --pack zero-trust
reportGenerate executive, audit, or incident reportsmaxlogic report generate --type exec --period 30d
rollbackUndo any automated action by its action IDmaxlogic rollback act_7f3c91

Case Files

Declassified incidents from MaxLogicBot’s service record.

CASE-0417Critical

Operation Glasswing

Credential stuffing turned into OAuth token abuse across 3 SaaS tenants at 03:12 UTC, when every human on the team was asleep.

  1. Impossible-travel sign-in flagged
  2. Malicious consent grant linked to the same session
  3. Tokens revoked, app consent removed
  4. On-call paged with full evidence pack
4m 51sto contain
0records exfiltrated
CASE-0388High

Silent Ledger

A service account that had been dormant for 212 days woke up and began moving laterally toward the finance database.

  1. Anomalous Kerberos ticket request
  2. 11-hop attack path to finance-db mapped
  3. Account disabled (human approved)
  4. 3 other dormant accounts found and disabled
6kill-chain stages
92%confidence
CASE-0352Critical

Night Shift

Ransomware precursors appeared on 2 endpoints: shadow copies deleted and backup agents killed.

  1. vssadmin delete shadows detected
  2. Matched to a known ransomware pre-encryption pattern
  3. Both hosts network-isolated via EDR
  4. Hosts reimaged and restored, no encryption
38sto isolate
0files encrypted

Enterprise Integrations

Unified data, automation, and visibility across your enterprise security and IT stack.

SIEM

Ingest, correlate, and analyze security events for detection and response.

SOAR

Orchestrate, automate, and execute incident response workflows at scale.

EDR

Endpoint detection and response for advanced threat prevention and containment.

Cloud

Multi-cloud security posture, workload protection, and misconfiguration detection.

Network

Network detection and response (NDR), traffic analytics, and lateral movement detection.

CI/CD

Secure software delivery with CI/CD security, code scanning, and supply chain risk management.

IAM

Identity and access management, privilege governance, and Zero Trust enforcement.

CMDB

Enterprise asset and configuration visibility to improve risk, impact analysis, and response.

Technical Specs

The numbers behind the helmet.

Event throughput
1.2M events/s sustained · 4.8M burst
Detection latency
p50 0.6s · p95 1.8s
Graph scale
38.6M entities · 412M relationships
Data retention
90 days hot · 2 years cold
Deployment
SaaS · self-hosted (Kubernetes) · air-gapped
Data residency
US · EU · APAC
Access
SSO (SAML/OIDC) · SCIM · RBAC with 14 built-in roles
Framework mapping
MITRE ATT&CK v15 · NIST CSF 2.0 · CIS Controls v8
API
REST + GraphQL · webhooks · 10k req/min per org
SDKs
Python · TypeScript · Go

Changelog

What MaxLogicBot learned recently.

  1. v4.7.2Latest
    • Kill-chain reconstruction is 34% faster
    • New Rego policy packs for identity hygiene
    • Fixed duplicate alerts on multi-region cloud trails
  2. v4.7.0
    • maxlogic ask: natural-language questions about your environment
    • Supervised autonomy (L3) is now generally available
  3. v4.6.0
    • Sentinel Graph 2: 4× entity capacity
    • Air-gapped deployment mode
  4. v4.5.0
    • Attack-path “what-if” fix simulation
    • One-click rollback for every automated action